Security Operations & Exposure Intelligence

What is exposed. What matters. What to fix first.

Prak Knit turns fragmented signals from the security tools you already run into one clear picture of exposure — across your enterprise estate and your AI — mapped to the business service at risk and the person who owns the fix.

AgentlessConnects with your existing toolsOn-prem & air-gapped options
app.prakknit.com — executive risk
Unauthenticated model endpoint · Payments APIteam-pay
KEV-listed RCE · Customer Portalweb-core
Exposed storage bucket · Analyticsdata-eng
Cleartext traffic · Mobile appmobile
One platform

One security context. Two attack surfaces.

Every organisation now has two estates to defend: the enterprise it has built, and the AI it is adopting. Prak Knit reads both through one context layer and answers in one risk model.

What you already runPrak Knit context layer
Enterprise signals
CloudApplicationsIAMVulnerabilitiesThreat modelsPentest
Klair VuEnterprise security & exposure
AI signals
AI servicesAgentsMCPModelsRAGTools
AI-InterceptorAI & agent security
One risk model
Prak Knit Unified risk model
  1. Deduplicate across tools
  2. Reachable & exploitable?
  3. Which business service?
  4. Who owns the fix?
What you get
Business exposureOne board-ready number, explained
An owned fix listRanked, with a named owner each
Work in your toolsInto Jira and ServiceNow

Read-only. No agent. Nothing to rip out. See the pipeline →

The problem

10,000 findings. Forty-three that matter.

Watch a quarter of findings collapse: duplicates merge, the unreachable fall away, and what is left is a queue a team can actually clear.

10,000This quarter
5,900After dedupe
700After exposure
43Worth this week

The deeper problem is that no tool answers what the board asks — are we exposed where it matters, and what do we fix first?

How it works

Uni-directional pipeline. No agent.

Each layer has a single job and a defined output — which is what lets a board number trace back to the scanner that raised it.

INSources

Your scanners, cloud, identity and tickets — read-only.

L1Normalise

One schema, one severity vocabulary.

L2Correlate

Dedupe, resolve assets, inherit ownership.

L3Score

Exposure + exploitation + criticality, explainable.

OUTAct

Prioritised work into Jira and ServiceNow.

Connects the signals you already run

SASTSCADASTCloudIdentityAPIDNSPentestThreat modelsGRC

No agent on your estate. Nothing to rip out. Switch Prak Knit off and every tool it reads from carries on exactly as before — the test of whether a platform is a layer or a lock-in.

See it

All risks, based on business context.

"Are we exposed where it matters?"

Business Posture leads with exploitable exposure to real business services — across IT, OT and AI — not a wall of counts. Read it as an exec, a CISO, an architect or for AI.
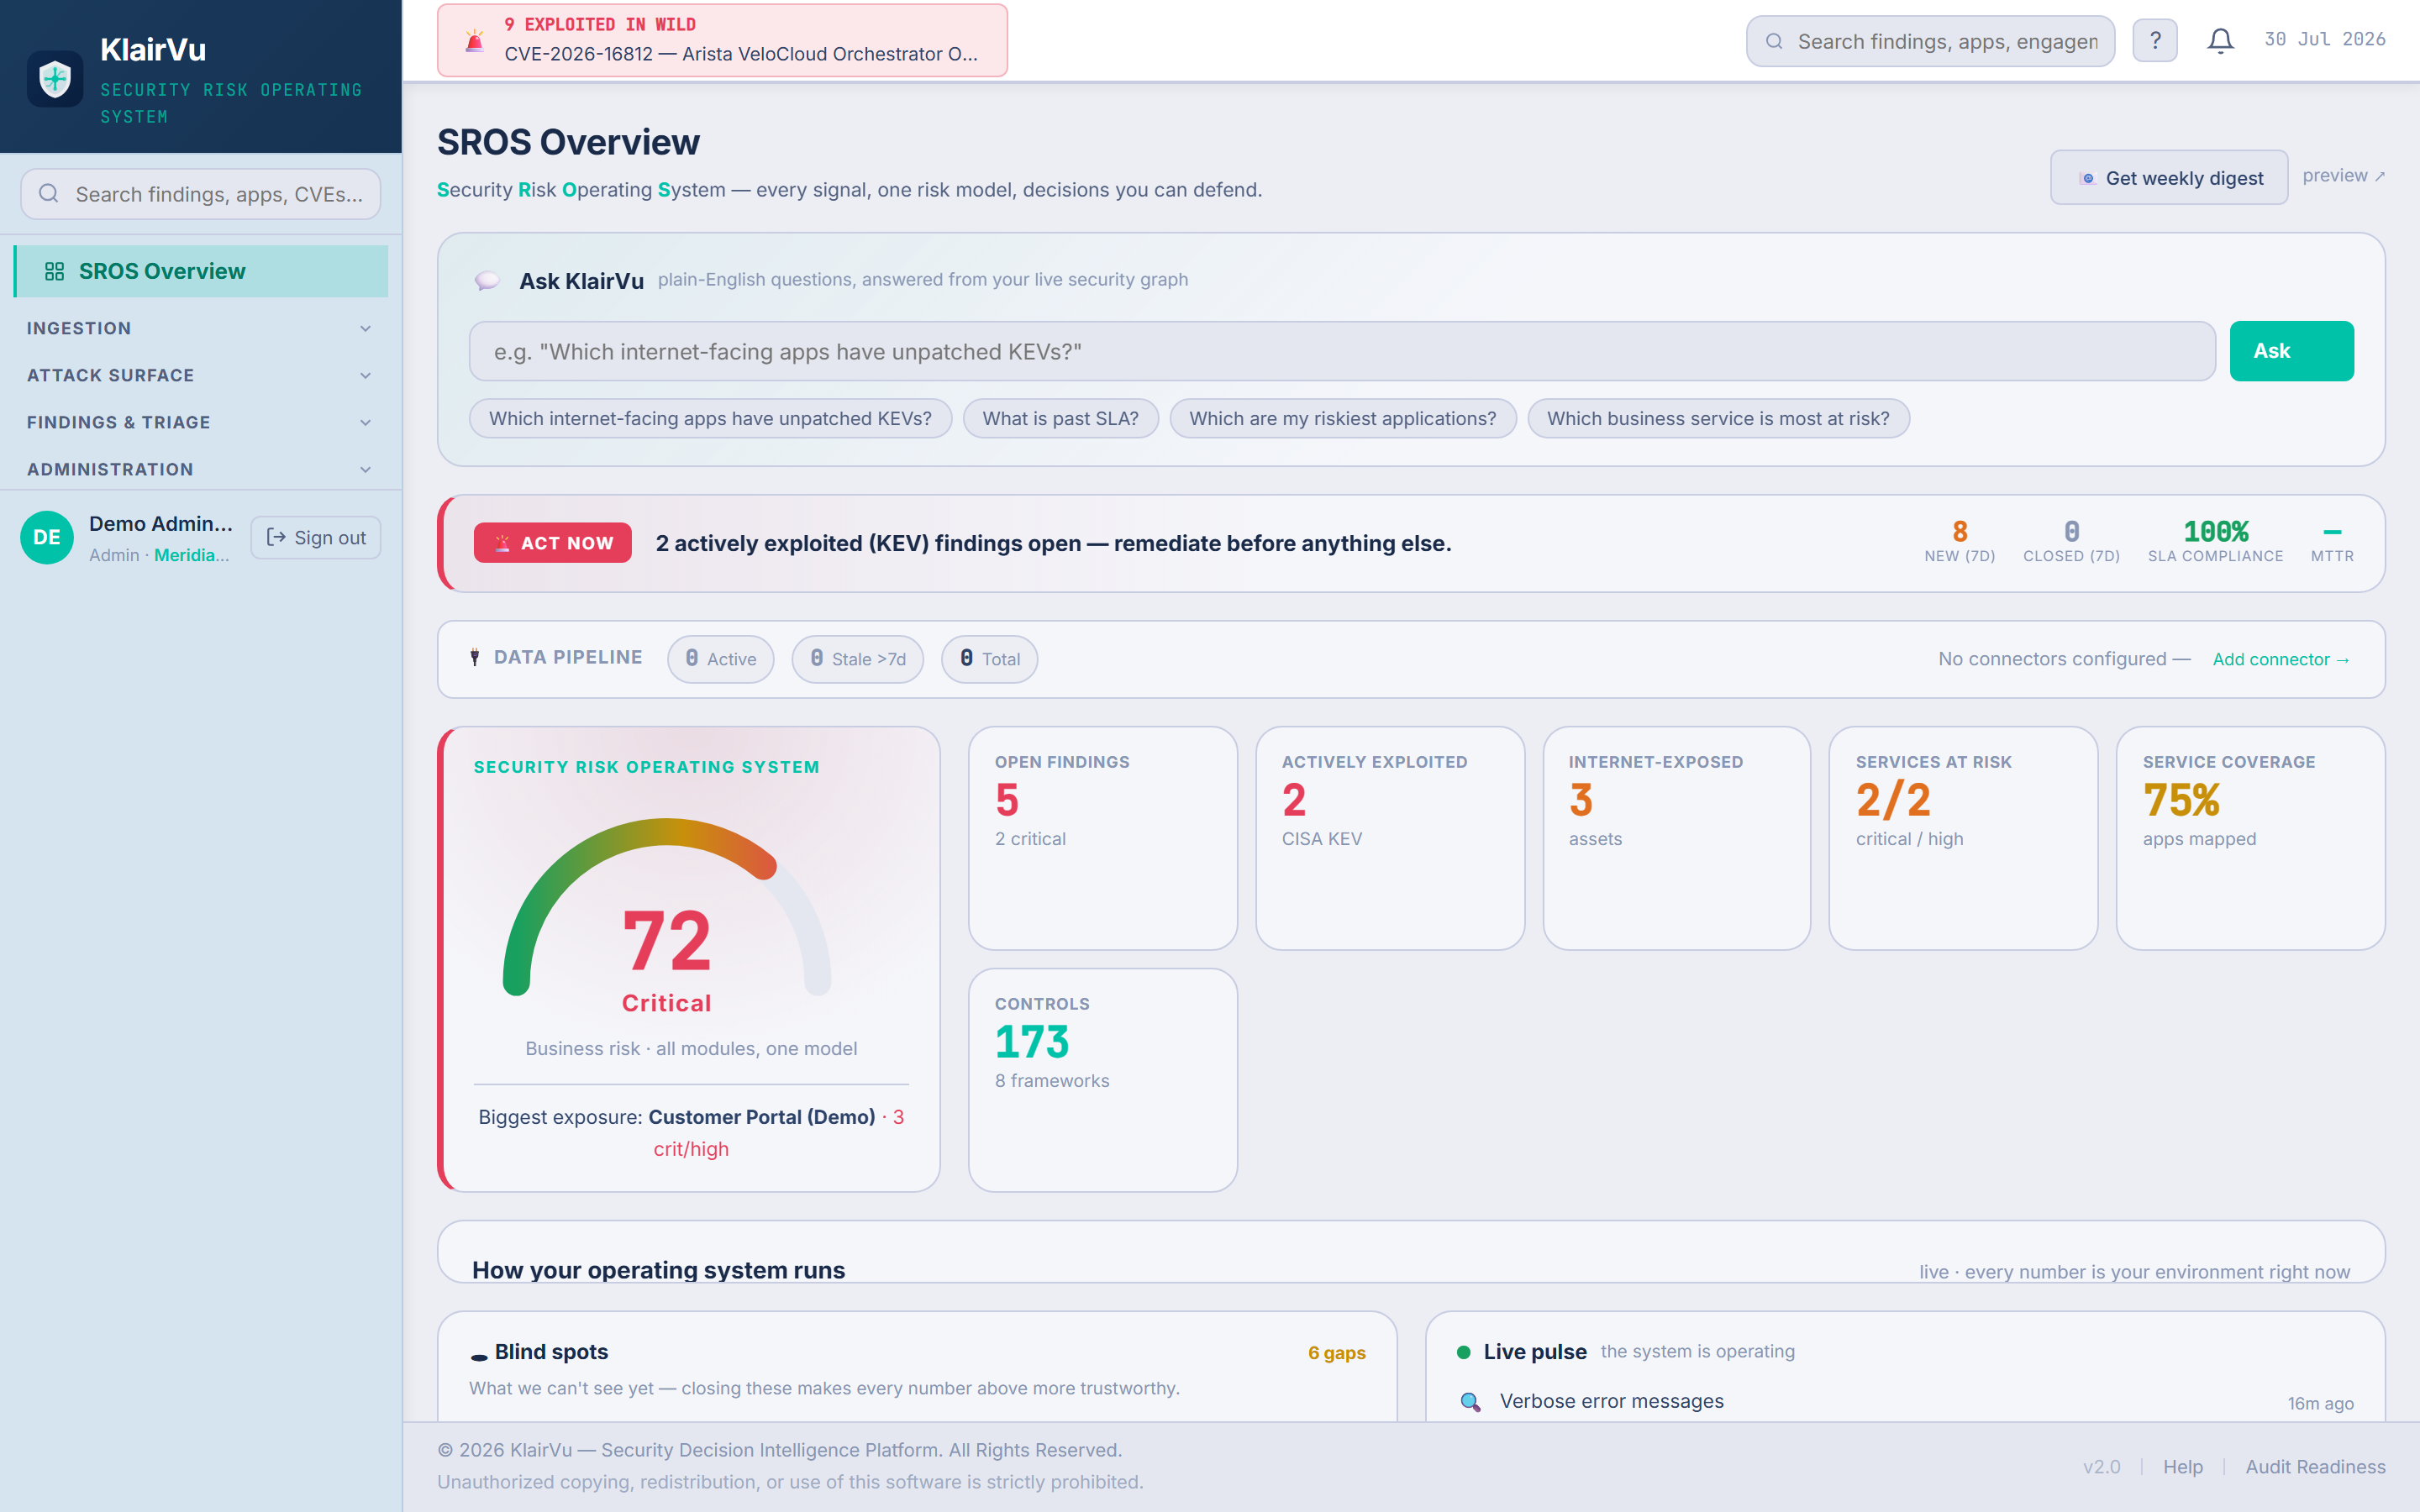
app.prakknit.com
Business Posture
Klair Vu Business Posture: business exposure across IT, OT and AI
"Where are all our findings?"

Every tool’s findings land on one page, each mapped to the application and business unit it affects — and duplicates collapse to one. The tool sprawl ends here.
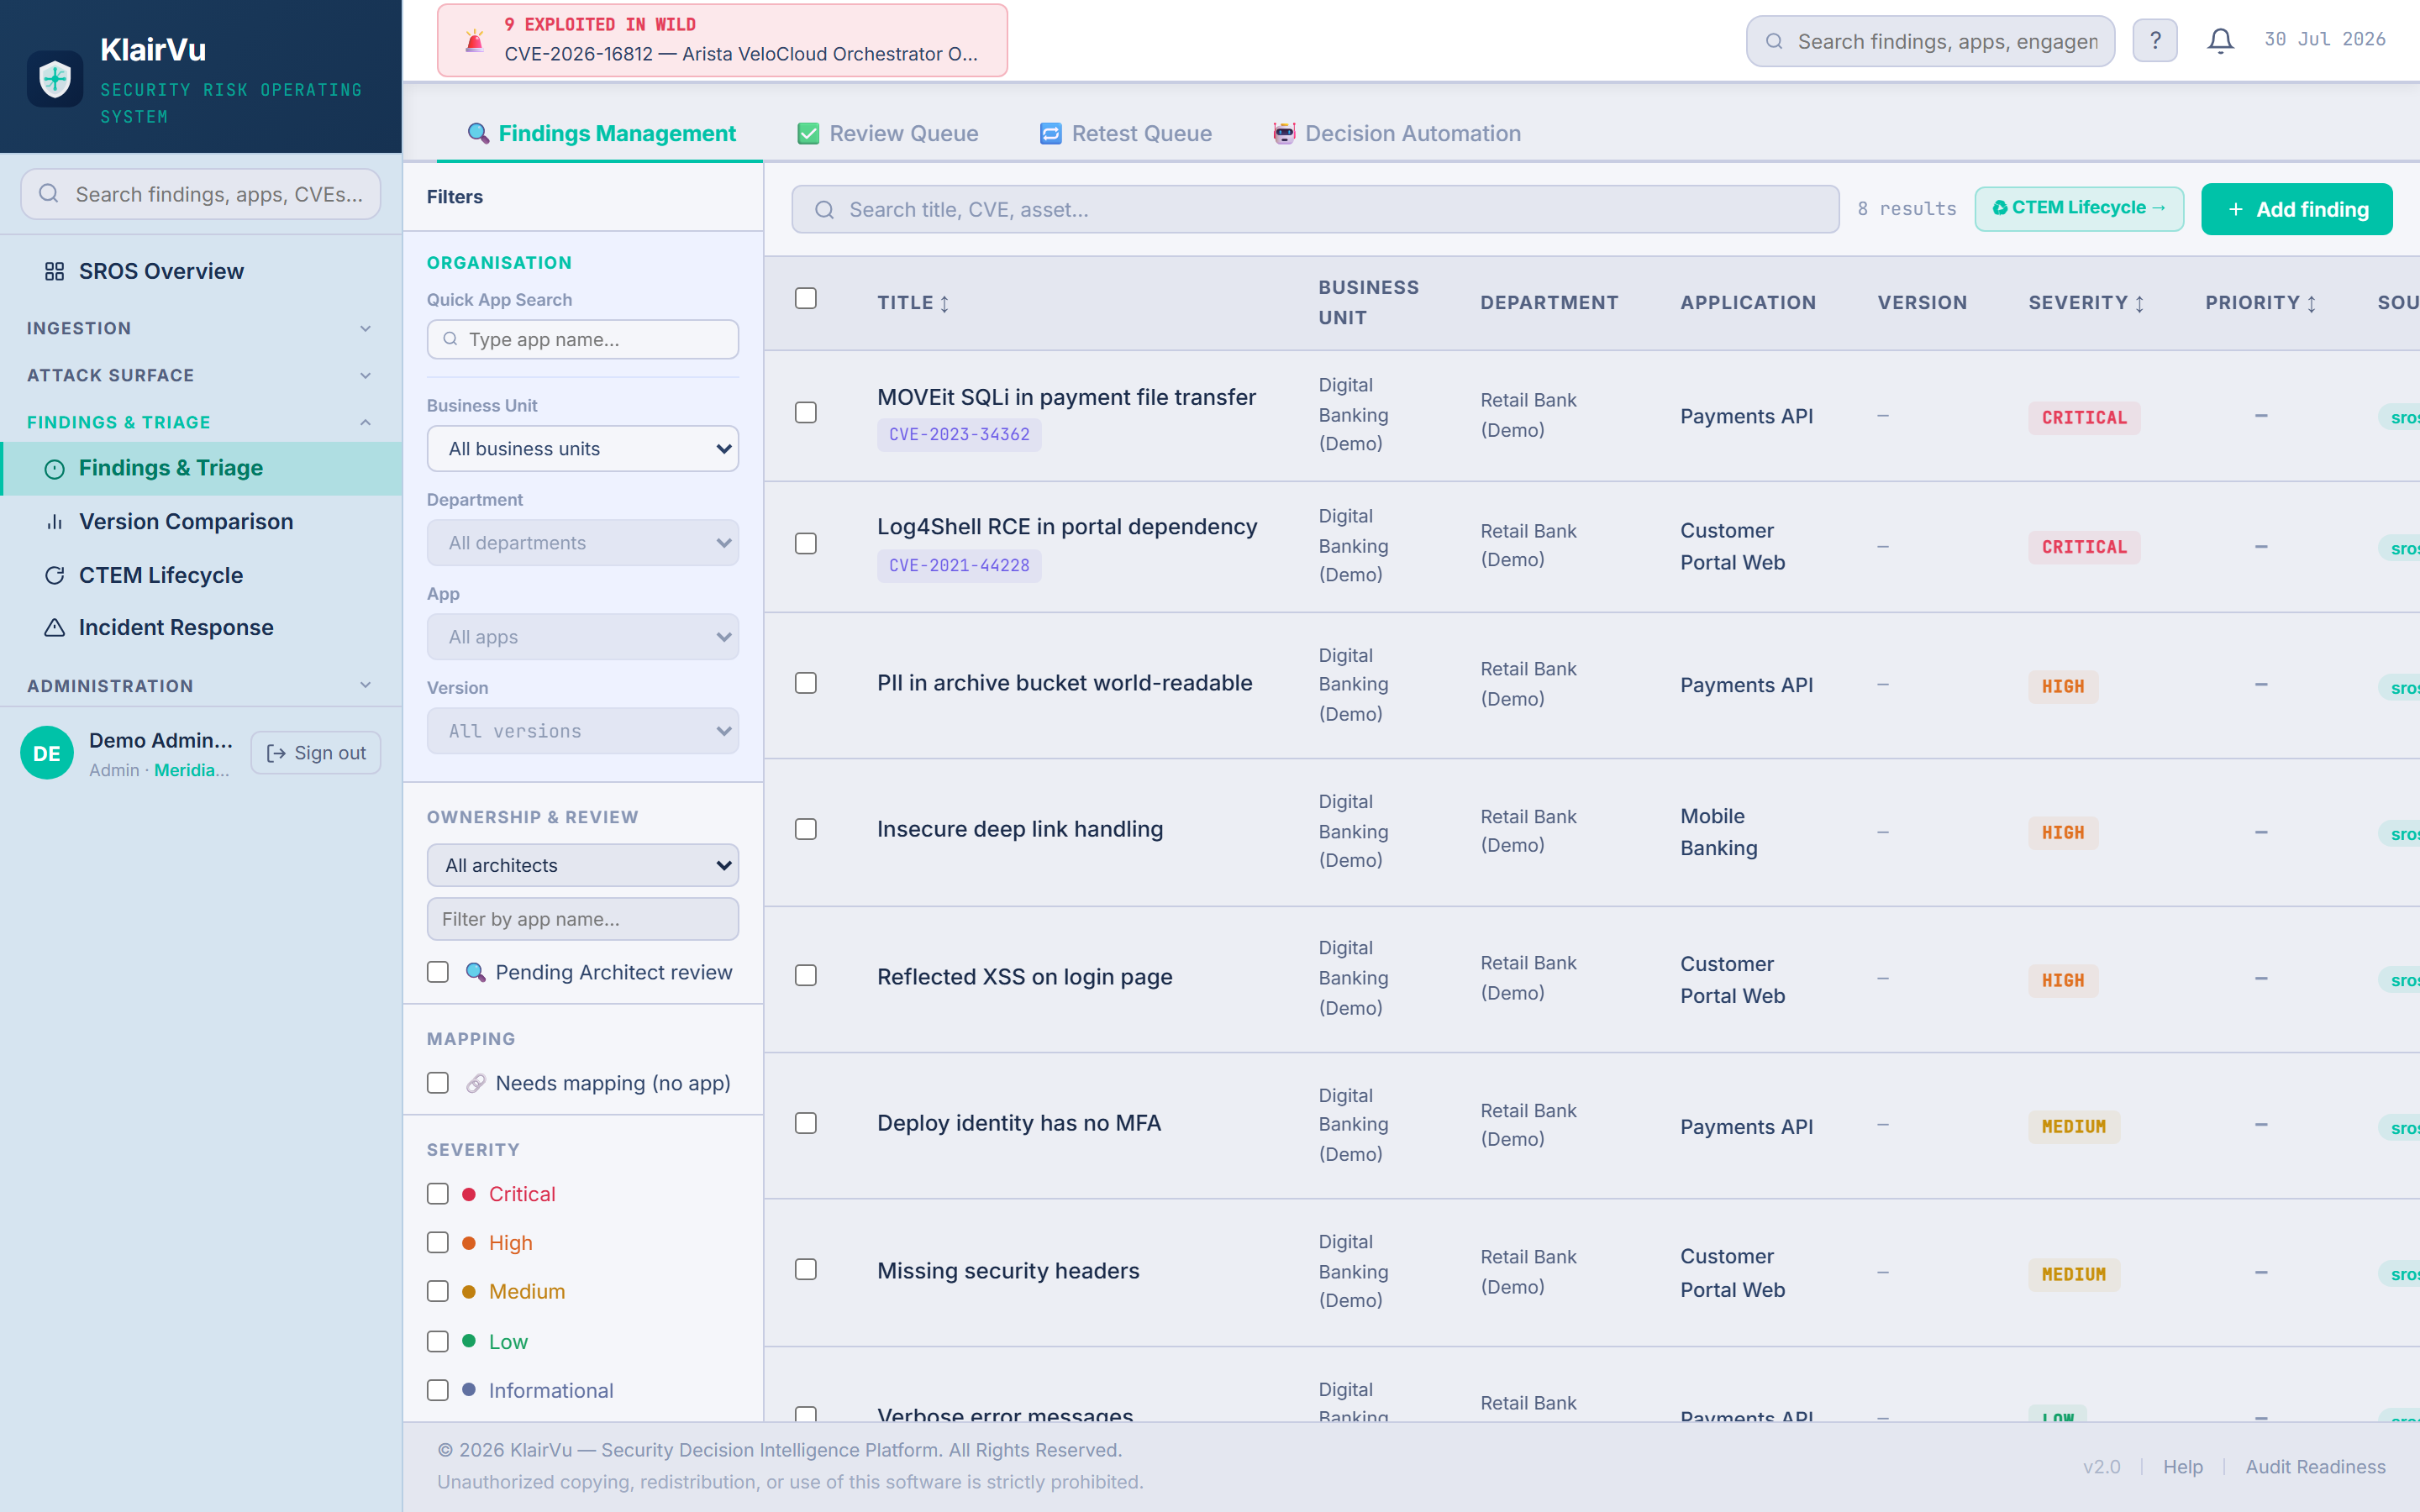
app.prakknit.com
Unified findings
Klair Vu findings queue mapped to business units and applications
"What can an attacker actually reach?"

Ask a plain question and get a real attack path as the answer: this exposure, plus that weakness, plus the architecture, chained end to end — the risk that lives in the seams between tools.
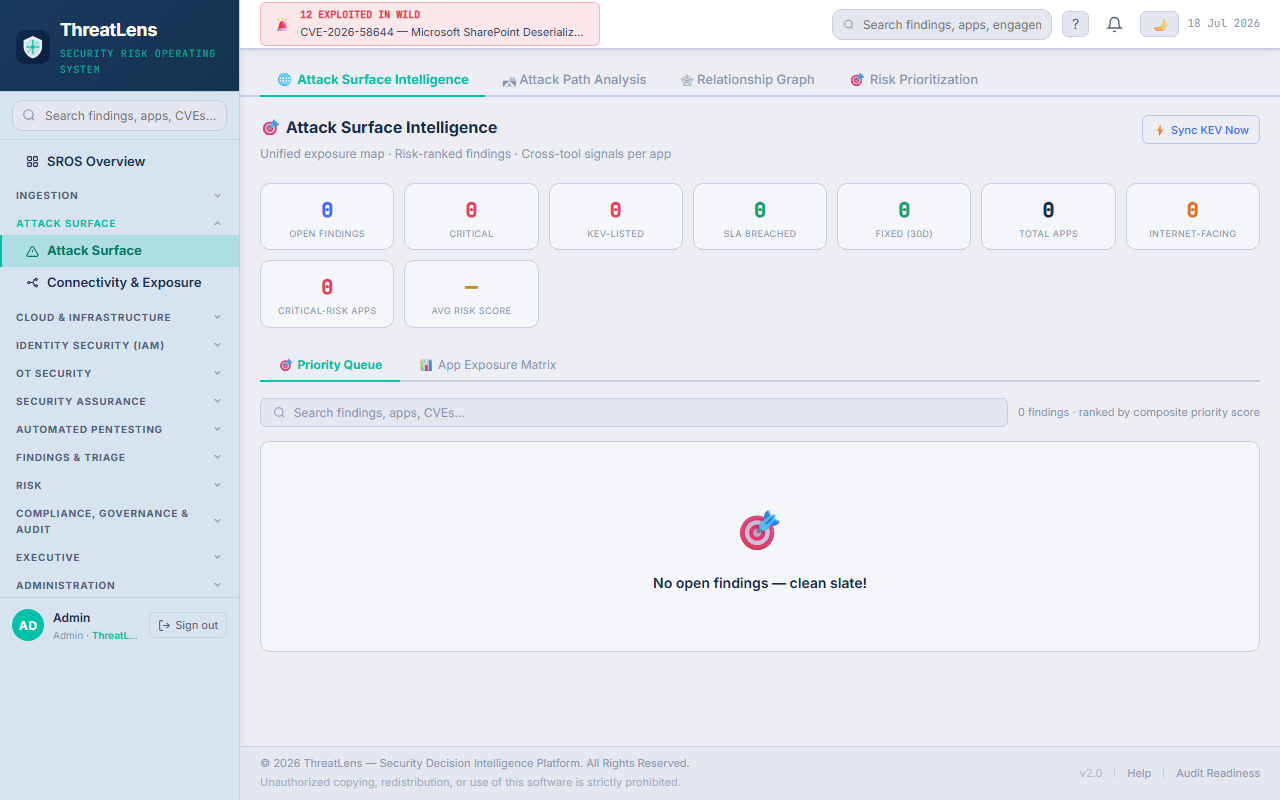
app.prakknit.com
Attack paths & intents
Klair Vu attack path from an internet-facing entry to a business service
"Is our AI exposed?"

AI-Interceptor discovers AI models and agents, maps what each one can reach, and flags the dangerous ones — the attack surface no existing tool covers.
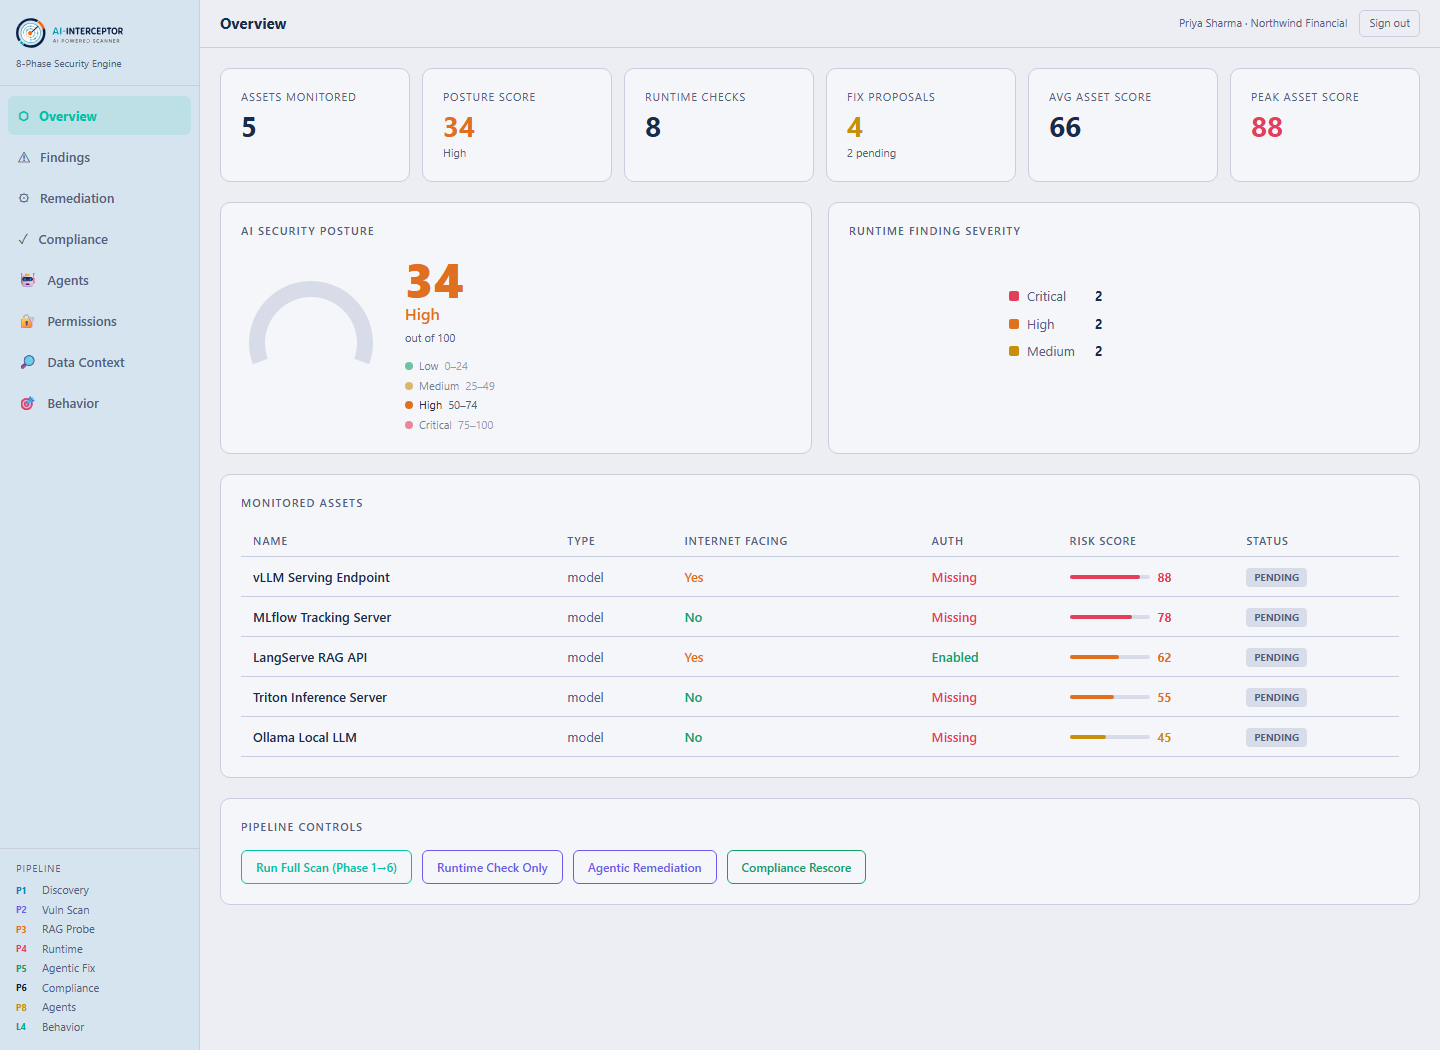
app.prakknit.com
AI-Interceptor
AI-Interceptor dashboard: AI assets, agents and critical AI risks
"Are we audit-ready?"

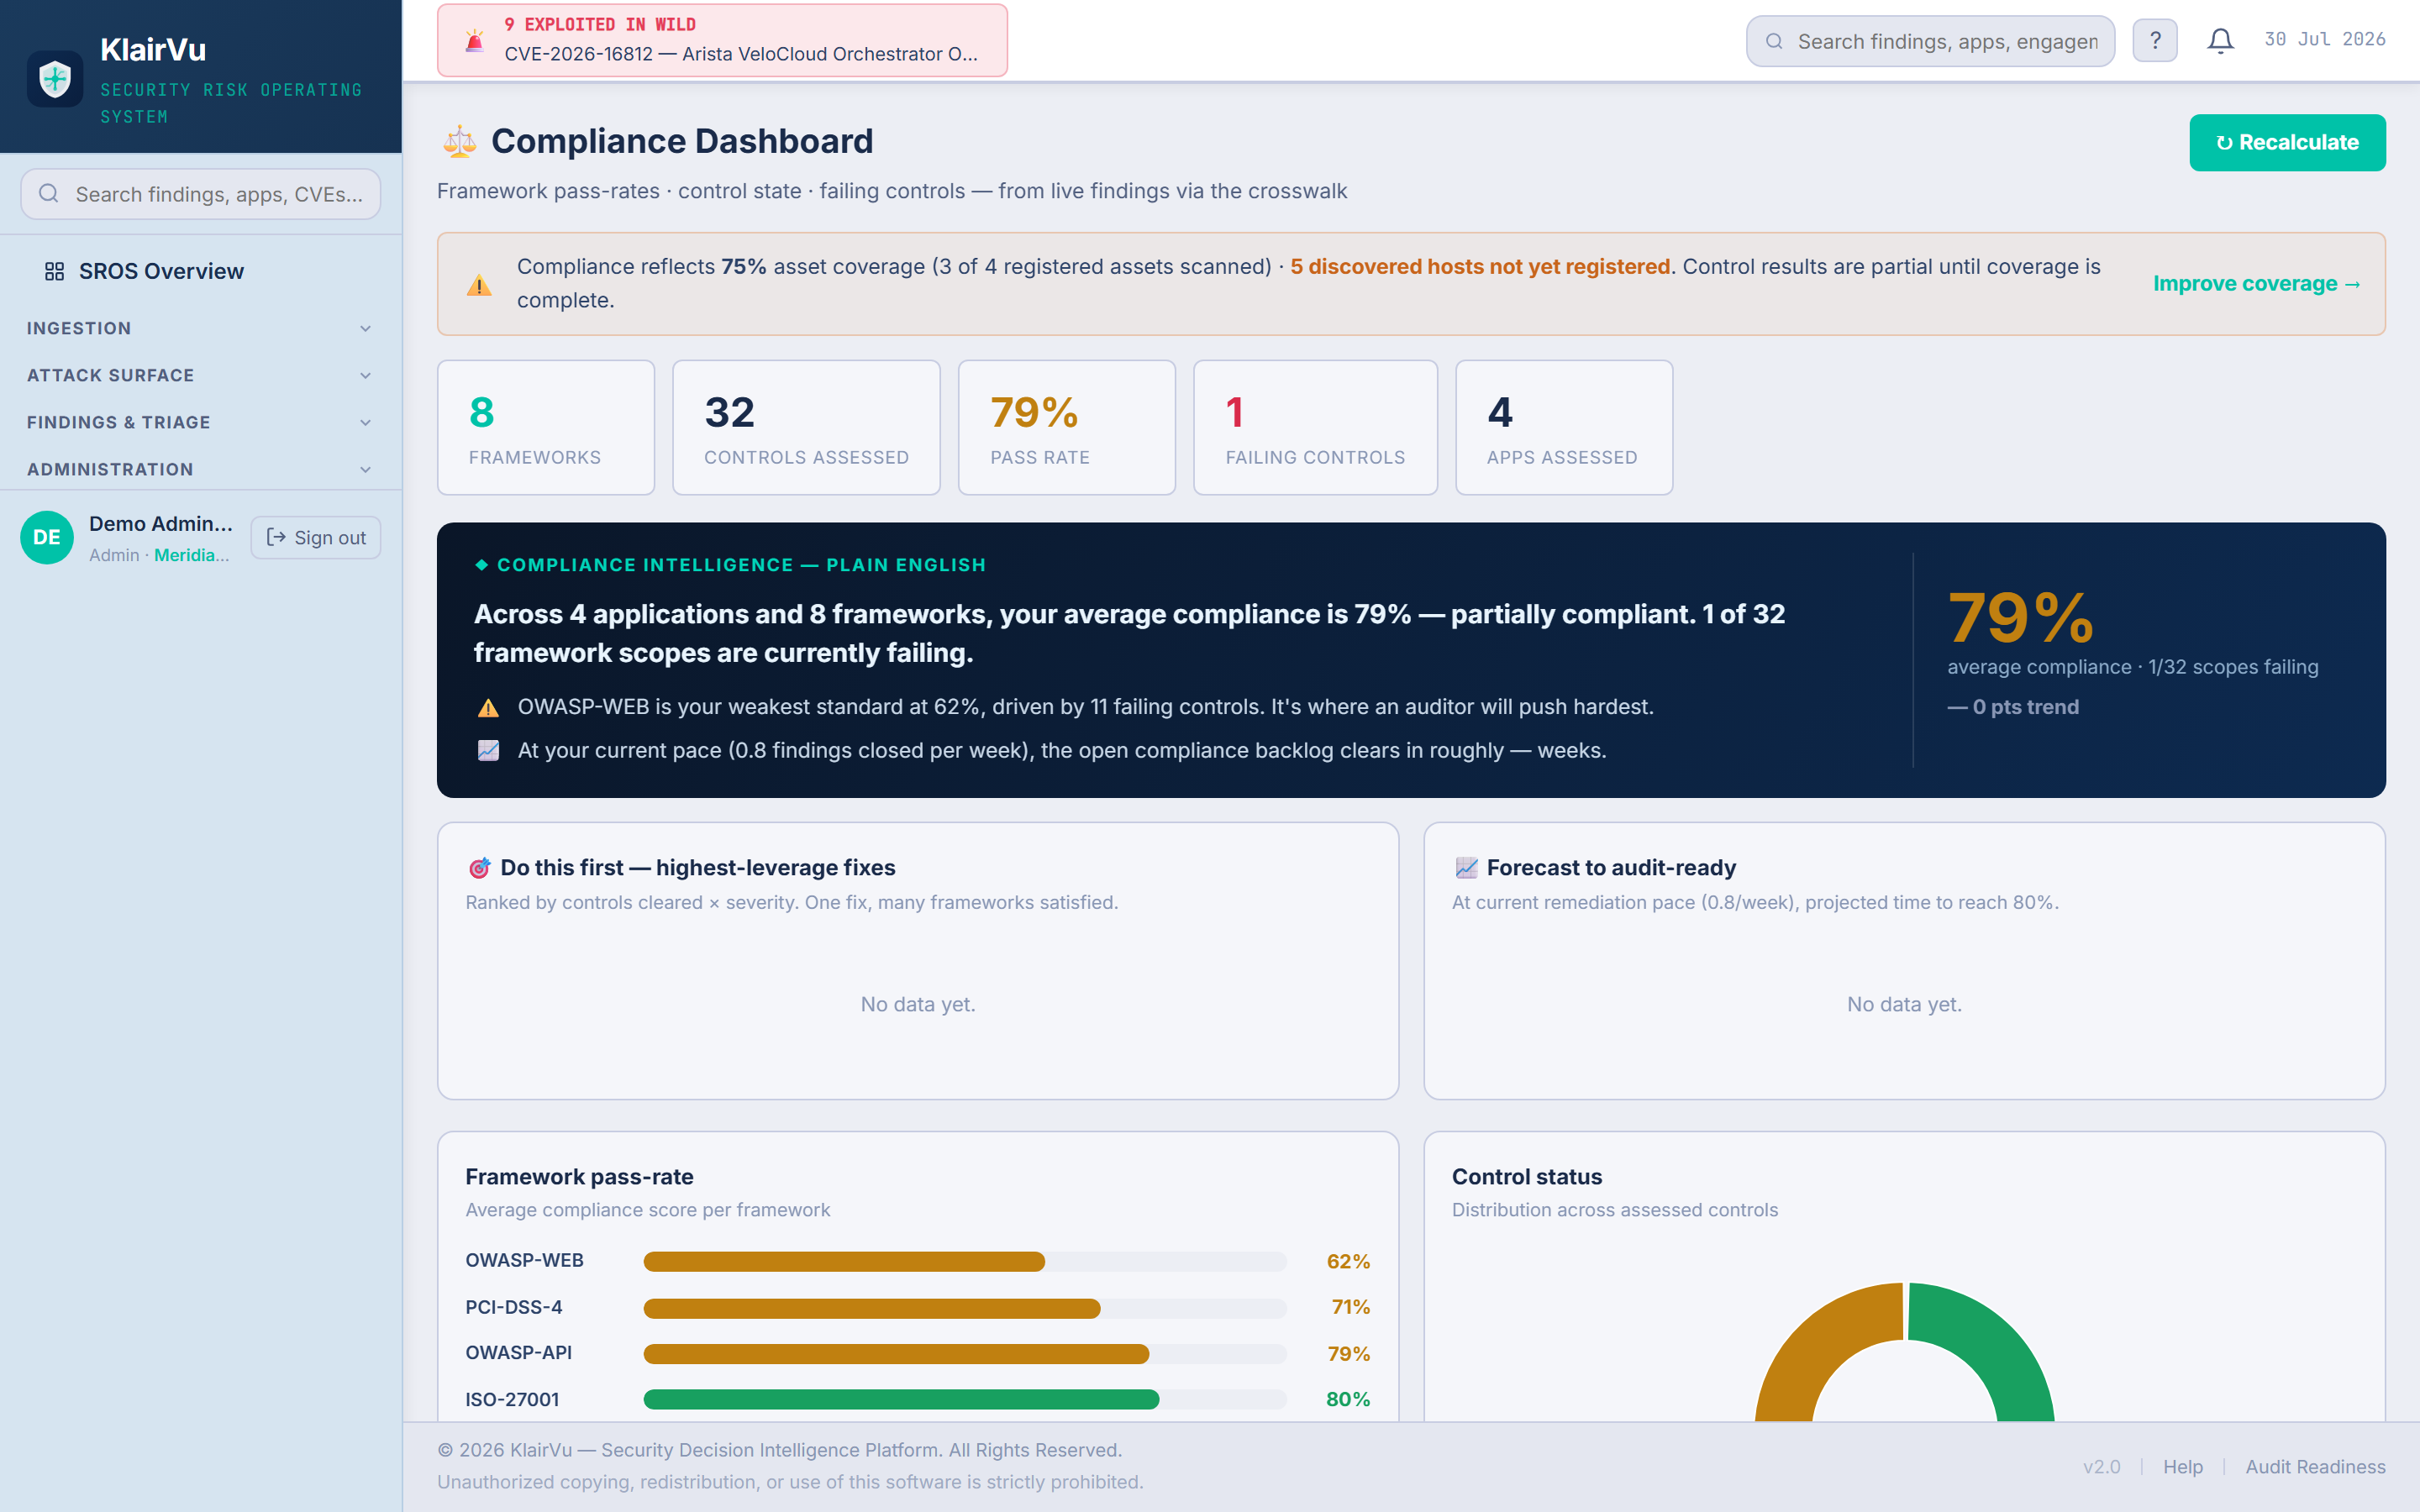
Compliance posture across frameworks, derived from live findings — with an honest coverage number that names the blind spots instead of showing a false pass.
app.prakknit.com
Compliance
Klair Vu compliance dashboard with honest coverage reporting
"Can the whole team work from one view?"

One sign-in replaces a wall of consoles. Everything your tools can see, scoped to your organisation, in a single place.
app.prakknit.com
One console, one sign-in
Klair Vu single sign-in

Captured from a live Klair Vu environment with demonstration data. Watch the five-minute tour →

Before you ask

You already have security tools. Keep them.

Prak Knit does not replace your investments; it connects their findings so leaders and engineers work on one priority.

ScannersFind weaknesses in their domain
CNAPPSecures the cloud
SIEMCorrelates events in time
CMDBHolds assets & ownership
Prak Knit

Unifies all four — into context driven outcome.

What you gain

RiskFix the few findings that can actually hurt a critical service — measurably lower real exposure.
ConfidenceA board-defensible risk number and audit-ready evidence, not a figure nobody trusts.
TimeTeams clear what matters instead of triaging thousands.
CostMore value from the tools you already own — nothing to rip out or replace.

None of them can answer the ultimate question "What is Monday's highest-leverage fix, and why?" — solving that requires unifying our telemetry, ownership graph, and control state. That unified context is the product.

Where do you stand?

Security maturity is how well your data informs a business decision.

A two-minute check of whether your programme can connect findings, ownership, and remediation priority. No email.

01
Tool visibilityFindings remain in individual security tools
Fragmented
02
Shared findingsTeams can see findings together, but duplicates remain
Aggregated
03
Clear ownershipRisks are linked to business services and accountable owners
Contextual
04
Business prioritiesExposure and criticality create a defensible remediation order
Prioritised
05
Decision-readySecurity, engineering, and leadership use the same risk picture
Aligned
See your risk visibility score

Answer for today’s environment. No email required.

Choose the statements that are true today.Your score shows the next practical improvement.
What you licence

Start with either surface. Both share one risk model.

Prak Knit product

Klair Vu

Enterprise Risk Intelligence

One business-aware view of enterprise cyber risk, with connected findings, accountable owners, and prioritised remediation.

Learn more →

Prak Knit product

AI-Interceptor

Enterprise AI Security

Discover unapproved AI services and identify which ones are reachable, exposed, or handling sensitive data.

Learn more →

Enterprise-ready

Built to survive its own assessment.

Strict per-tenant data isolation

Every customer's data is kept strictly separate, and that separation is tested on every release.

Your data stays your data

Never shared or used to train models. SSO, SCIM and RBAC included; on-prem and air-gapped options.

Evidence, not assurances

A tamper-evident audit trail and encrypted backups, with architecture details available under NDA; correlation logic informed by real enterprise threat-modelling.

Maps your risk to

RBI CSFISO 27001SOC 2HIPAANIST CSFIEC 62443

Bring a question your tooling answers badly.

45 minutes. A straight answer about coverage — including what we do not cover.

One business day to a reply. No sequence, no drip campaign. Prefer to read first? Start with our whitepapers.